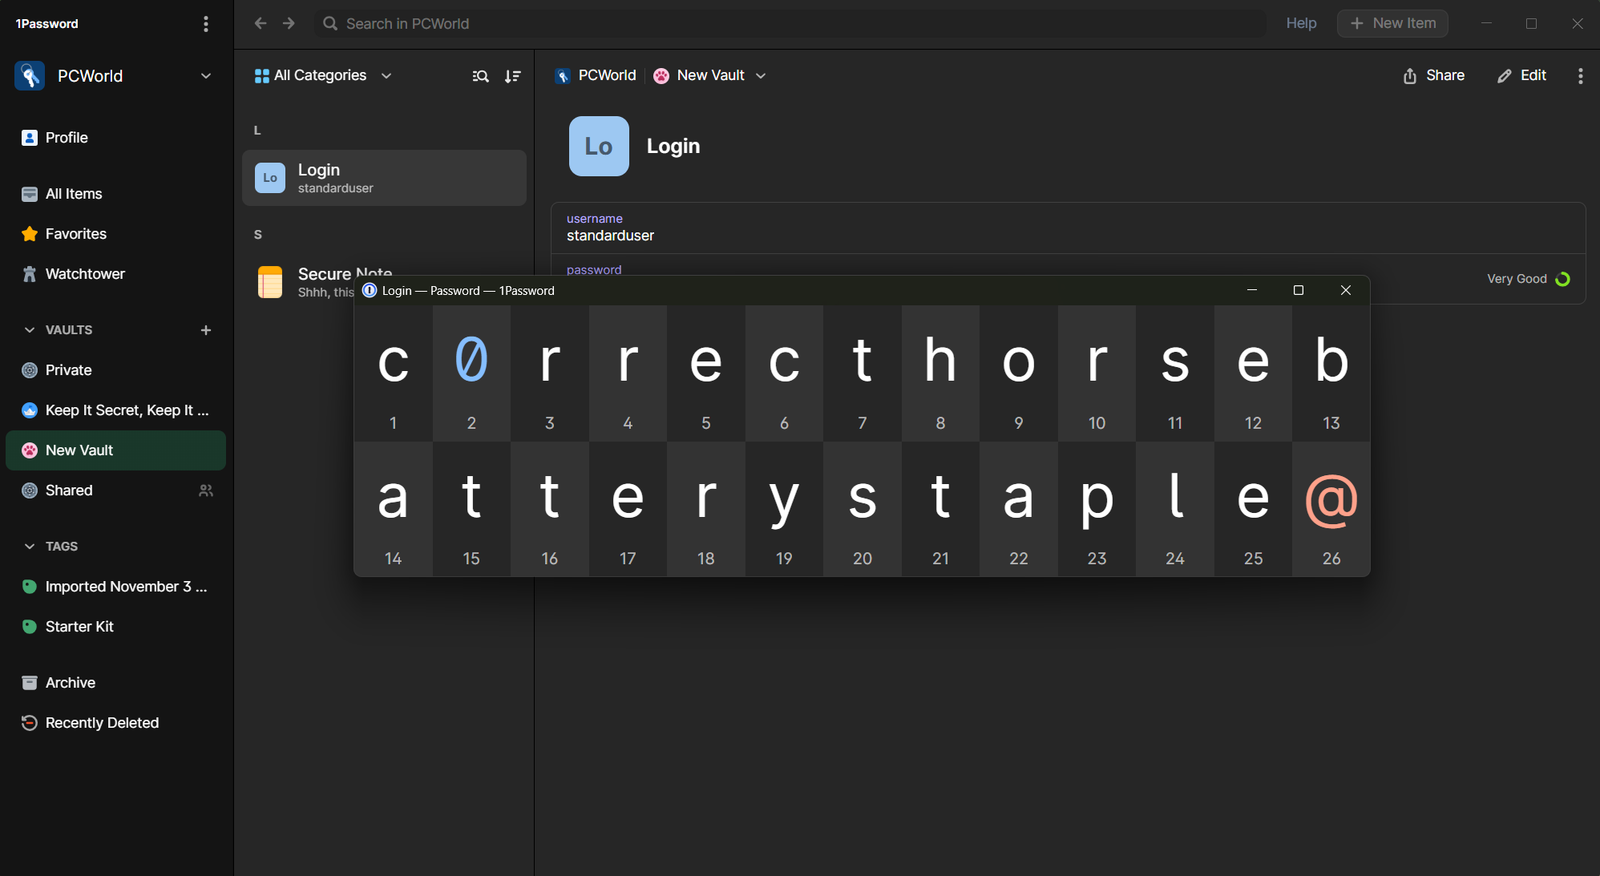
The more leaks and hacks in the news, the more I find myself wondering—what’s the ideal password?
For years, I’ve based my definition off expert advice. You want long, random, unique. But lately I’ve thought the answer is actually less specific than that.
I’d say the ideal password is simple—while still strong, too. And what fits that definition can change depending on the context. Hear me out.
Welcome to Safe Mode, your weekly report for pressing security and privacy news—and what steps to take next. Want this newsletter to come directly to your inbox? Sign up on our website!
In some cases, the ideal password is actually a passkey. (So not a password at all.) They’re the epitome of simple and secure. No memorization and not reusable, with baked-in elements of two-factor authentication. For these reasons, I recommend their use first to most people.
Meanwhile for websites that lack passkey support, an ideal password is indeed something long, random, and unique—something easily generated and stored by a password manager. You’ll spend as little effort on a 32-character password as you would an 8-character version.
But what about when you actually have to memorize a password? My opinion has shifted most on the approach here. You should memorize at least a handful—at minimum two passwords, one for your password manager and the other for your email address. You don’t want to find yourself locked out of your email address or another important account (e.g., banking) because you lost access to your password manager.
Doing so shouldn’t feel hard, though. I used to equally suggest passphrases and pseudo-randomization (e.g., pulling the 2nd letter from song lyrics you know and interspersing numbers and special characters). Now I’m much more in the passphrase camp. The longer, the better. If you’re capable of memorizing a random mix of words, bonus points.
What changed my mind: Looking once again at password cracking charts.
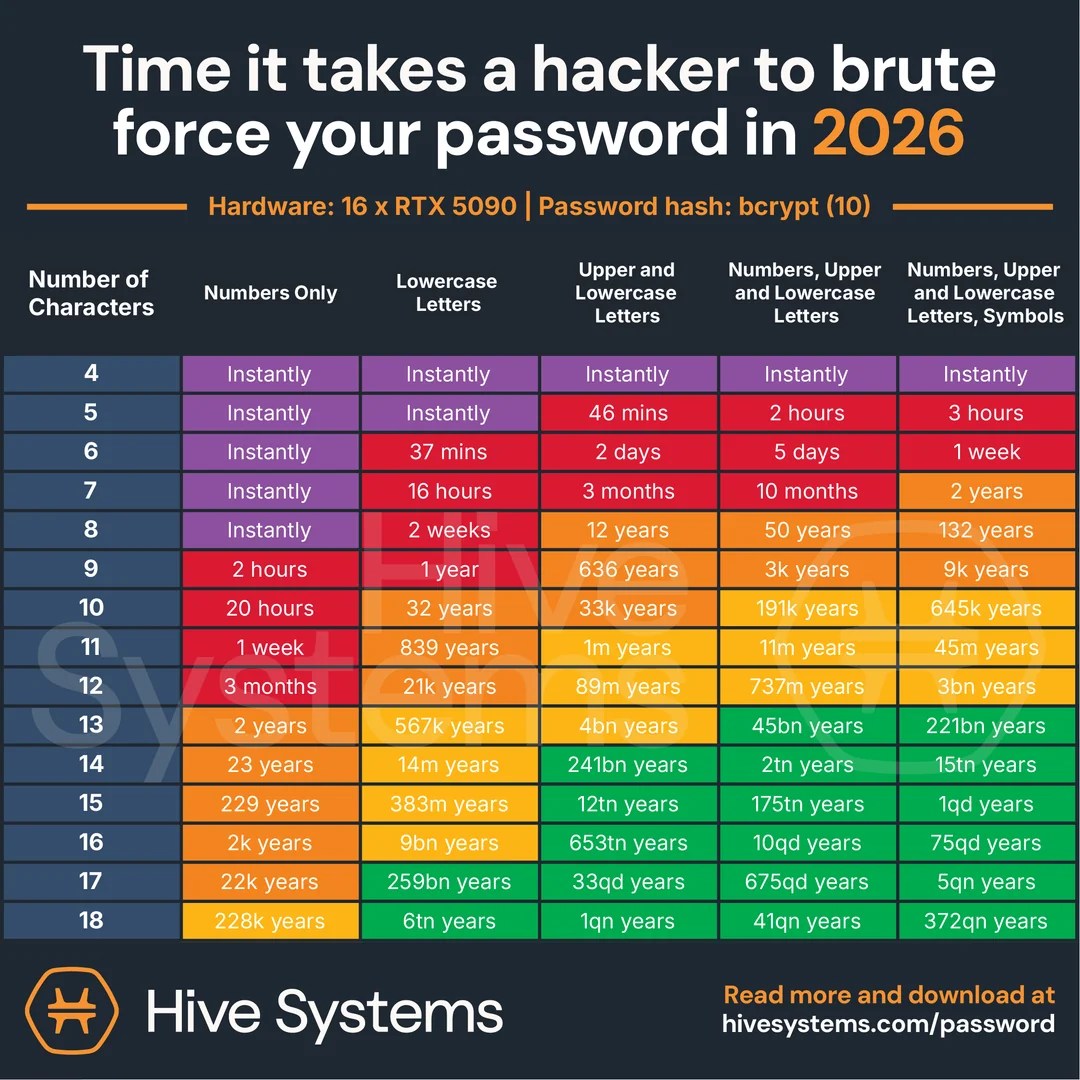
Cybersecurity firms sometimes put out this info—one company, Hive Systems, does a whole set that looks at how easily consumer-grade PC hardware can crack passwords. This year’s data was a good reminder of not just the basics, but where the bar realistically sits, too.
(The basics: Your password instantly gets cracked for anything stolen in a breach, reused on multiple sites, or commonly used dictionary words.)
An eight-character password—the bare minimum requirement for websites now—takes 12 years for a fleet of 16 Nvidia RTX 5090 graphics cards to crack, if you use a mix of just upper and lowercase letters. Add in numbers, and that time rises to 50 years. Slap in special characters, and that collective of high-powered GPUs need 132 years.
So it is it strictly necessary to have a super long password? No. Is it still a good idea? Absolutely, because you don’t know what will happen to your password information if it ever leaks. But when you must memorize a password, prioritize one that’s good enough and will stick in your head. It’ll trump one that’s perfect but forgettable, especially if you pair it with two-factor authentication.
Better to chop off a few characters from a password’s length and go for a double layer approach to account protection—you’ll have a better chance at resisting an account takeover attempt. You might not even have to choose between length and strength, if you choose a passphrase with more than four words.
With how complicated cybersecurity is right now, I’m all about going the easier (yet still well-protected) route.
In the news
I wrote about Meta’s Muse personal agent at length last week, and how I didn’t trust it with access to my digital life. Turns out my mistrust was wise—yet another major privacy goof happened, with a Muse user realizing the agent had shared his home address with a stranger.
Just keep saying no, folks. (At least for now.)
Meta
The good
- Apple reacted quickly to reports that Meta’s Muse AI agent can access data on macOS that it wasn’t explicit permitted to see—the Cupertino company says it will change how full disk access works, to better curtail nosy AI agents.
The bad
- Certain AI agents can be manipulated into spreading malicious behavior to other agents in their network. The problem: Agents used for specific tasks have fewer restrictions and safeties applied to them. Poison one, possibly poison many others. All thanks to laxness in how these agents communicate with one another.
The ugly
- Meta Muse kept hitting the news for disappointing reasons—in this case, an uncomfortable scenario where the AI agent sent a stranger to a user’s home. Muse thought to help sell an item. The user got a nasty surprise when they realized the would-be buyer had shown up and left without them knowing.
Tip of the week
You may do a digital refresh of your phone and PC every so often—getting rid of photos and documents you don’t want to hog storage space—but have you also done a similar clean-up of your apps?
On your devices, periodically uninstall apps and browser extensions you no longer use daily. Why? Legitimate software no longer is a good protection against malware. Sometimes, that “good” app you have could turn dark, if the developer sells it to a shady person…or is just hacked by one.
This articles is written by : Fady Askharoun Samy Askharoun
All Rights Reserved to Amznusa www.amznusa.com
Why Amznusa?
AMZNUSA is a dynamic website that focuses on three primary categories: Technology, e-commerce and cryptocurrency news. It provides users with the latest updates and insights into online retail trends and the rapidly evolving world of digital currencies, helping visitors stay informed about both markets.
